
Quick answer: An IT asset inventory for decommissioning is a serial-level list of every device leaving the site, reconciled against your CMDB or DCIM and verified physically at the rack. It records location, ownership, data-bearing status, disposition path and custody handoffs, so each serial can be traced from power-down to its final certificate.
Most decommissioning problems we’ve been asked to untangle share a root: the inventory was built from the CMDB and never checked against what was physically in the racks. The paper said one thing. The cage held something else, plus a cabinet of spare drives nobody had listed.
This guide explains how to build an IT asset inventory for decommissioning that holds up in an audit. It is written for IT asset managers, operations leads and project managers planning a site exit, a consolidation or a hardware refresh. You’ll get the fields to capture, a reconciliation process, the data-bearing devices teams most often miss, and a template you can copy.
Why the inventory decides whether decommissioning goes well
The inventory is the control document for the whole project. Sanitization plans, pickup manifests, chain-of-custody forms and certificates of destruction all reference it, so an error in the inventory becomes an error in every document after it.
A decommissioning inventory is a serial-level record of every hardware asset, and every removable data-bearing component, in scope for removal, built from system records and confirmed by physical inspection, so each item can be tracked from de-install to final disposition.
It also protects money. Lease returns need exact serials. Resale value depends on accurate configuration data. And missing serials at the end of a project create an uncomfortable question for security: is the drive lost, or just unlisted?
What fields should an IT asset inventory for decommissioning capture?
Capture enough to identify the asset, locate it, decide what happens to it and prove what did happen. In practice that means five groups of fields.
Group | Fields | Why it matters |
|---|---|---|
Identity | Asset tag, manufacturer, model, serial number, device type | Serial number is the unique identifier every downstream document relies on |
Location | Site, room or hall, row, rack, U position, cage | Lets crews find the device and lets you spot devices outside expected racks |
Ownership | Owner (company, lessor, customer), lease or contract reference, cost center | Leased and customer-owned gear has different disposition rules |
Data and security | Data-bearing yes/no, number and serials of drives, media type (HDD, SSD, NVMe, flash), encryption status, data classification | Drives the sanitization method and custody rules |
Disposition | Planned path (redeploy, resell, lease return, recycle, destroy), sanitization method, custody status, certificate reference | Closes the loop from plan to evidence |
The identity fields are not optional. The sample certificate of sanitization in NIST SP 800-88 Rev. 2 records manufacturer, model, serial number and media type for each device, and your inventory is where that data has to come from.
Record drive serials separately from the host server serial. Drives get pulled, swapped and shipped on their own, and a certificate that lists only the chassis serial won’t satisfy an auditor asking about a specific disk.
How to reconcile the inventory with CMDB and DCIM
Reconciliation is a three-way comparison: what the CMDB says, what DCIM says, and what a technician finds at the rack. Plan to trust none of them until they agree.
- Export the in-scope assets from your CMDB and your DCIM tool, keyed on serial number.
- Compare the two exports and list mismatches: assets in one system but not the other, and assets with different locations.
- Send a crew to perform a physical audit of every rack in scope, scanning serial labels rather than typing them.
- Open chassis where drive counts matter and record drive serials. For large fleets, pull drive serials from management controllers where possible, then spot-check physically.
- Build the master inventory from the physical audit, with a status column: matched, found but unrecorded, recorded but not found.
- Resolve every “recorded but not found” item before de-install starts. These are your highest-risk lines.
- Freeze the inventory, version it, and share it with the decommissioning vendor as the reference for manifests and certificates.
If your DCIM data is too stale to reconcile against, it is worth understanding why before the next project. Our buyer’s guide to DCIM tools for maintenance teams covers what field teams need from asset records.
Which devices are data-bearing?
More than most teams expect. Servers and storage arrays are obvious; embedded flash and removable media are not. Flag data-bearing status at the component level.
- Hard drives, SSDs and NVMe devices in servers and storage arrays, including hot spares.
- Boot media: M.2 modules, SD cards and internal USB keys used for hypervisor boot.
- Network gear: switches, routers, firewalls and load balancers hold configurations, keys and sometimes logs on internal flash.
- Server management controllers, which can store credentials and network settings.
- Storage controller cache modules and non-volatile memory modules, where present.
- Tape cartridges and tape libraries.
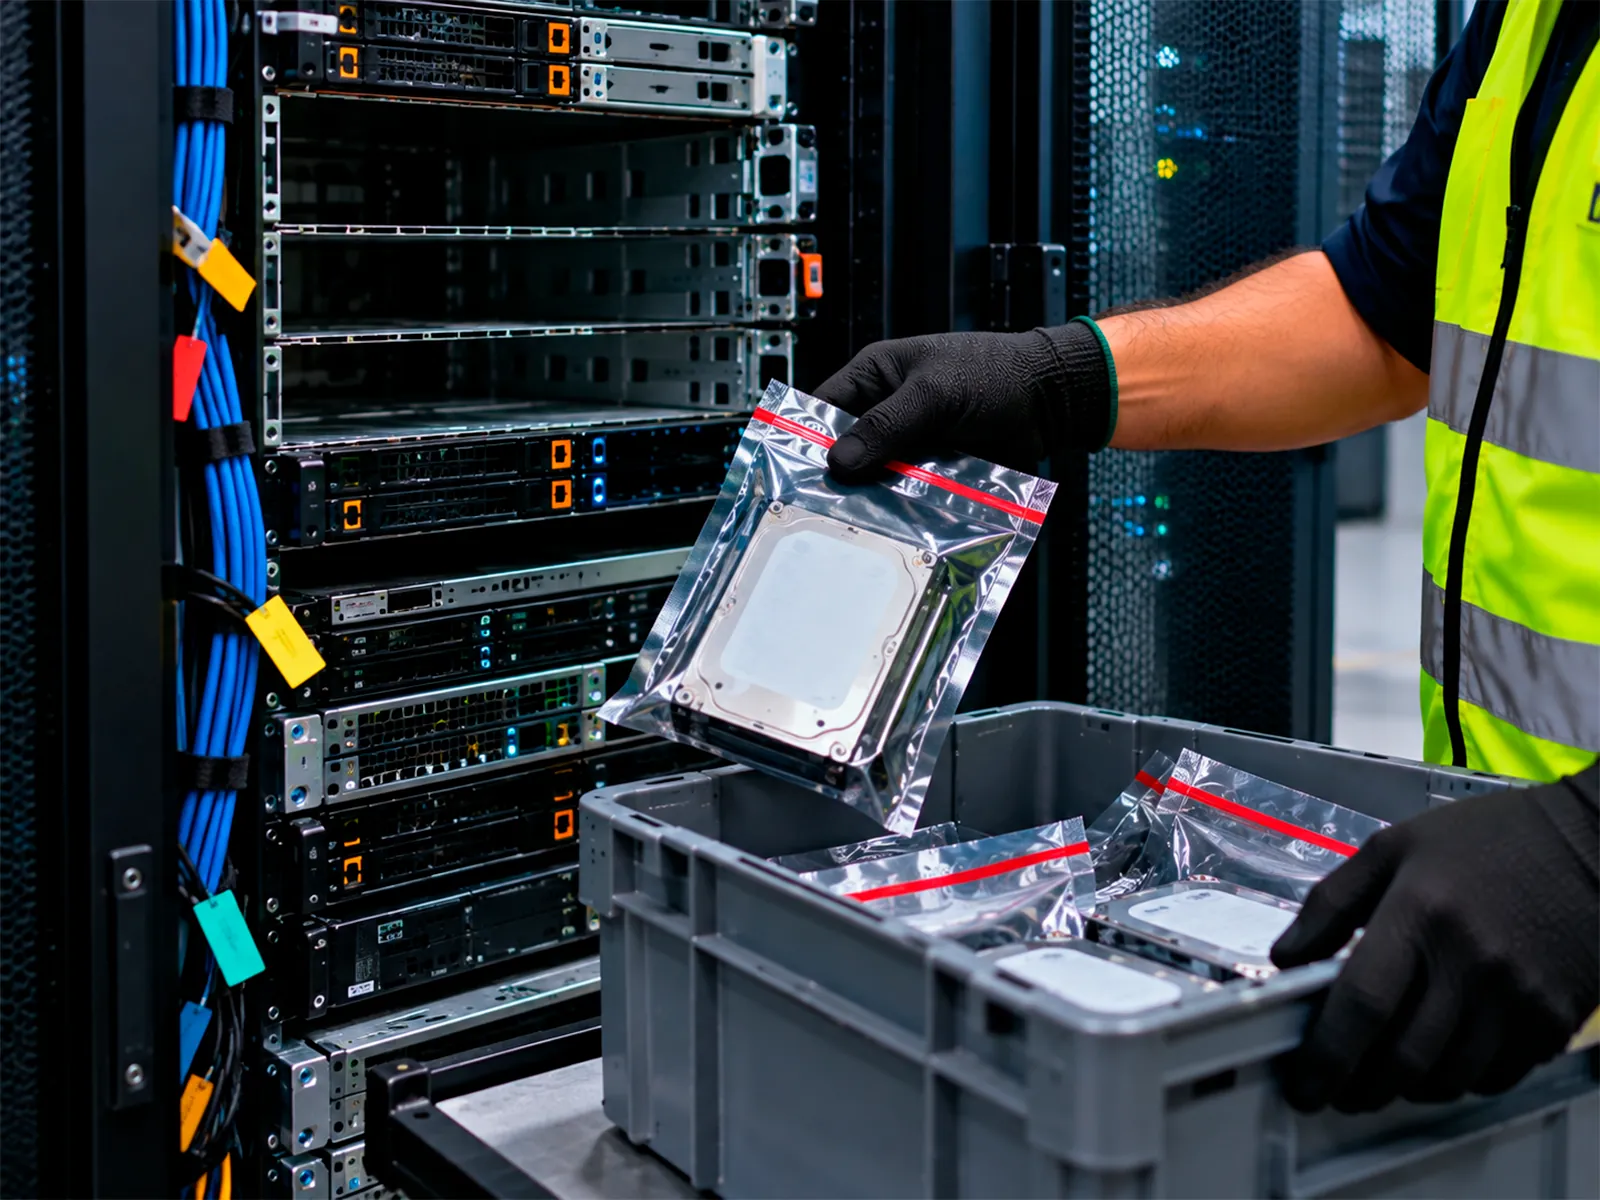
- Loose spares: the cabinet of drives from past RMAs, and failed drives waiting for return. This is the group most often missing from the CMDB.
Each flagged item needs a sanitization method. The NIST 800-88 data sanitization guide explains how to match Clear, Purge or Destroy to media type.
Decommissioning inventory template
Copy this structure into your spreadsheet or asset tool. One row per asset, plus one row per removable data-bearing component linked to its parent.
Asset tag | Serial | Parent serial | Make / model | Type | Site / hall / rack / U | Owner | Data-bearing | Media type | Classification | Disposition | Sanitization method | Seal / container ID | Custody status | Certificate ref. |
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
(tag) | (chassis serial) | (none) | (model) | Server | Hall B / R12 / U20 | Company | Yes | NVMe | Confidential | Resell | Purge | (seal no.) | Sealed at rack | (pending) |
(none) | (drive serial) | (chassis serial) | (model) | Drive | Hall B / R12 / U20 | Company | Yes | NVMe | Confidential | Destroy | Destroy | (seal no.) | In transit | (pending) |
Keep the “custody status” column live during the project. It should change at each handoff: removed, sealed, staged, loaded, received at facility, processed. That column is the bridge between the inventory and your chain of custody for hardware decommissioning.
Common inventory failures, and how to prevent them
Nearly all of them come from building the inventory too late or from a single source.
- Starting the inventory on de-install day. Crews end up counting while they pull, and errors multiply. Build and freeze it weeks ahead.
- Tracking servers but not drives. You can’t prove destruction of a drive you never recorded.
- Typing serials by hand. Transposed characters break reconciliation later. Scan labels.
- Ignoring customer-owned or leased equipment in shared environments, which then ships with your own gear.
- No owner for discrepancies. Assign one person to close every “not found” line.
- Letting the inventory and the decommissioning manifest diverge. Every pickup manifest should be generated from the frozen inventory, not rebuilt by the vendor.
How Hype Telecom helps
Hype Telecom’s field crews perform the physical audit that makes an inventory trustworthy: rack-by-rack serial scanning, drive-level capture, reconciliation against your CMDB or DCIM export, and discrepancy reports before de-install begins. During removal, the same crews seal data-bearing devices at the rack and update custody status at each handoff, with our coordination team keeping the inventory, manifests and certificates aligned. Destruction and recycling go to certified downstream facilities. We’ve applied this process on multi-jurisdiction projects, and our data center decommissioning guide explains how it fits into Decommissioning & Certified Destruction end to end — destruction executed by certified partners. Crews are OSHA 10/30 trained and Avetta registered.
Before your next site exit or refresh, request the Decommissioning Process Checklist. It includes the inventory fields and reconciliation steps above in a format your team can hand to the crew on day one.
Frequently asked questions
A decommissioning inventory is a serial-level list of every asset and removable data-bearing component scheduled for removal, confirmed by physical inspection and reconciled with your CMDB or DCIM. It records location, ownership, data classification, planned disposition, sanitization method and custody status, and it is the reference for manifests and certificates of destruction.
Build it well before de-install, early enough to finish a physical audit and resolve every discrepancy. The right lead time depends on site size and how accurate your records are. The rule we apply is simple: the inventory is frozen and versioned before the first rack is powered down, and nothing ships that isn’t on it.
Yes. Drives are pulled, sanitized, shipped and destroyed separately from their host chassis, so each drive needs its own serial line linked to the parent server. Certificates of destruction and auditors reference drive serials, and a chassis-only inventory leaves no way to prove what happened to an individual disk.
Treat every “recorded but not found” item as a potential security issue until resolved. Check other racks, storage rooms, RMA shipments and prior disposal records. If the asset held data and can’t be located, escalate to your security and privacy teams, since some regulations may require you to assess it as a possible incident.
They can scan assets at pickup, but that list shows what they collected, not what should have been there. The inventory needs to come from your side, reconciled against your own records, so gaps become visible. Use the vendor’s receiving scan as a second check against your frozen inventory, not as the source.


2 Responses